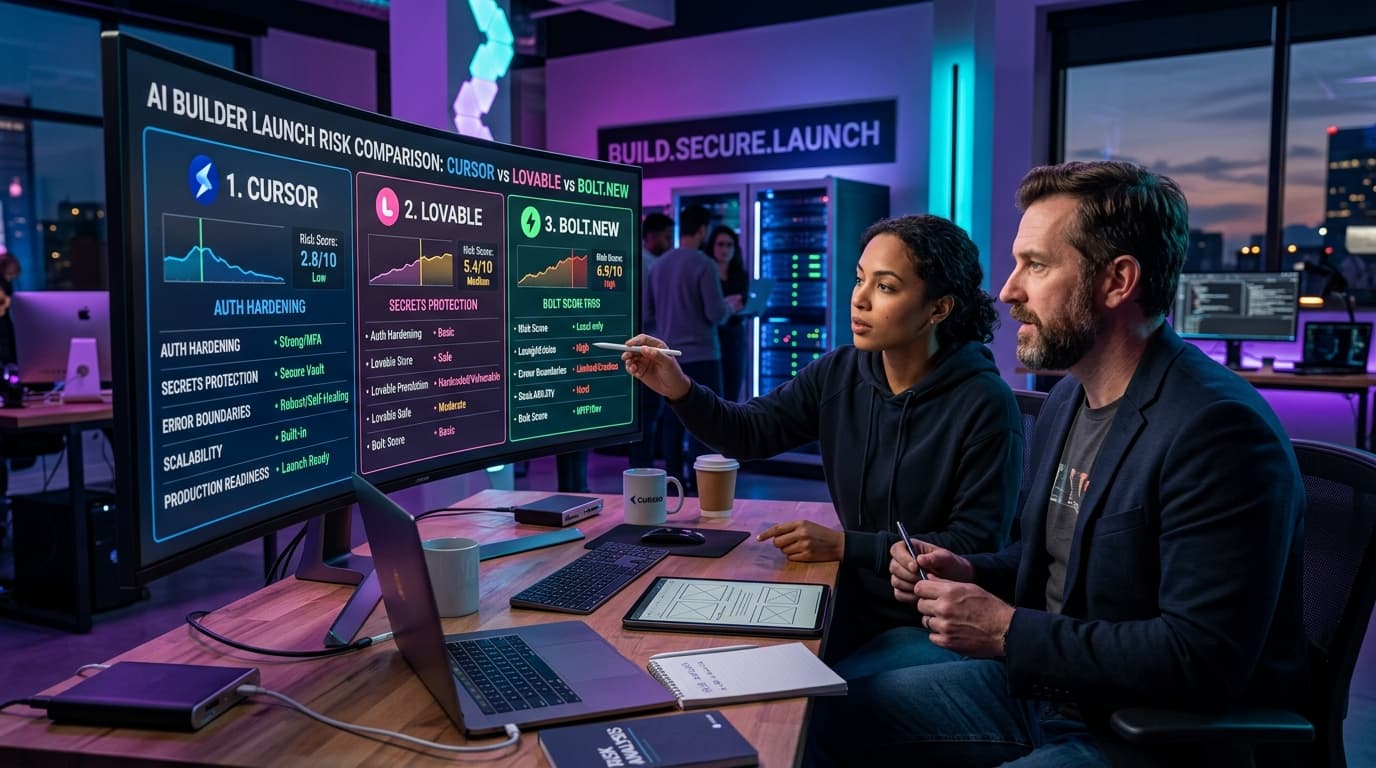
Why Tool Choice Affects Launch Risk (Not Just Build Speed)
Founders are shipping faster than ever. You can spin up a product with an AI builder in a single weekend, get early beta users excited, and push straight to production. But launch day often exposes hidden risk: authentication flows leaking session tokens, environment variables baked into the client-side JavaScript bundle, and apps crumbling under a modest Product Hunt traffic spike. The speed was real. The risk was invisible.
Every AI builder makes fundamental architectural tradeoffs. A tool optimized purely for generation speed will offload critical security decisions to the founder without making that handover obvious. A tool optimized for drag-and-drop convenience can abstract away low-level infrastructure details that require direct founder control before launch.
The Dangerous Middle Ground: The biggest risk in vibe coding is a product that feels production-ready because the UI looks immaculate and the demo works. But beneath the surface: API responses expose raw database stack traces, endpoints lack rate limiting, and database credentials are stored in ways a senior security engineer would reject. If you want to audit what you have already built, start with a professional technical audit before opening the gates to production traffic.
The five risk categories below represent the exact fault lines where AI builders diverge most sharply. Let's break down how Cursor, Lovable, Bolt.new, and Replit stack up when real users and real money are on the line.
AUDIT FRAMEWORK
The 5 Launch-Risk Categories That Differ Across AI Builders
These are practical, real-world launch concerns—not abstract engineering theory. Each category maps to an operational failure mode capable of hurting users, damaging founder reputation, or forcing an emergency week-two rewrite.
01Authentication Defaults
Does the tool produce hardened auth out of the box, or does it generate functional-looking patterns that cut corners on JWT expiration, refresh token rotation, and RBAC permissions?
02Data & Secret Handling
How are database keys and third-party API credentials isolated? Can sensitive production credentials accidentally leak into client-side browser bundles?
03Error Management & Exposure
When an unhandled exception triggers, does the app fail gracefully with clear user copy, or does it leak internal database schemas and raw stack traces to the public?
04Concurrency & Scalability
Can the generated data architecture survive 500 simultaneous users without pool exhaustion, or is it hardcoded for zero-scale single-user demo environments?
05GTM & Observability Readiness
Does the scaffold include Open Graph meta tags, canonical URL routing, Core Web Vitals optimizations, and error telemetry hooks—or is the GTM layer completely absent?
TOOL PROFILE 1 • DEVELOPER-LED ACCELERATOR
Cursor: What It Leaves to the Developer and Founder
Cursor is an AI-enhanced IDE, not a vibe-coding playground. That distinction matters immensely. You write real code inside a real Git repository; Cursor simply helps you write it faster. The output quality, security posture, and architectural soundness depend entirely on your prompt specificity and code-review discipline.
Authentication: High Flexibility, Zero Guardrails
If you prompt for Supabase Auth or NextAuth.js with explicit session rotation, Cursor produces clean, robust code. But if a non-technical founder asks for “a simple login system,” Cursor will gladly generate a naive JWT implementation with hardcoded fallback secrets, no refresh rotation, and no server-side invalidation. Cursor will never warn you that your auth is dangerously insecure.
Data Handling & Secrets: Developer Hygiene Required
Cursor operates directly in your local environment and reads your .env files for context. If you paste API keys into chat prompts or reference client-side components incorrectly, Cursor will not stop you from compiling sensitive tokens into your public client bundle.
Scalability & GTM: Highest Ceiling, Manual Setup
Scalability is Cursor's greatest strength. Because you own the standard Next.js, Node, or Python codebase, you have zero architectural lock-in. However, Cursor will never spontaneously build Open Graph tags, canonical URLs, or PostHog telemetry hooks unless you explicitly instruct it.
TOOL PROFILE 2 • FULL-STACK NATURAL LANGUAGE BUILDER
Lovable: What It Manages and What It Leaves Exposed
Lovable scaffolds full-stack applications from natural language prompts. Its target audience is founders who want a working product without navigating complex CLI setups or local Docker containers. That convenience dictates its unique risk profile.
Authentication: Strong Supabase Foundation, Policy Blind Spots
Lovable natively integrates Supabase Auth, which means you receive real authentication rather than a toy prototype. Row-Level Security (RLS) is enabled by default. The critical launch risk arises when founders assume default RLS covers their specific multi-tenant data model. Having RLS turned on is useless if the policy is configured as USING (true), allowing any authenticated user to read all database records.
Data Handling & Abstraction: Harder to Inspect
Lovable abstracts away file systems during prototyping. While this speeds up screen generation, it makes auditing environment variables and API routes harder for non-technical founders. Webhook verification secrets for Stripe or payment providers frequently end up misconfigured.
Scalability: Database Connection Bottlenecks
Lovable apps rely heavily on direct Supabase client connections. Under a Product Hunt launch spike, hundreds of users hitting the app simultaneously will exhaust Postgres connections unless connection pooling (PgBouncer) is explicitly configured.
TOOL PROFILE 3 • ZERO-TO-ONE SPEED PROTOTYPING
Bolt.new: The Fastest Path and Its Hidden Tradeoffs
Bolt.new is unmatched in generation velocity. Type a prompt, and a functional browser-based WebContainer app appears within seconds. But launch risk is directly proportional to how little friction the tool imposes.
Data Handling: Highest Secret Exposure Risk
Bolt.new is the highest-risk tool for credential leakage among all AI builders. Because it generates client-side focused stacks in WebContainers, it routinely bakes third-party secrets (OpenAI API keys, Stripe private keys, Resend tokens) directly into client bundles where anyone inspecting the network tab can extract them.
Authentication: Demo-Grade Sessions
Authentication in Bolt.new apps often relies on localStorage tokens or mock backend handlers. It works flawlessly when demoing on a single laptop, but fails catastrophically under multi-device sync, session timeouts, or concurrent user signups.
Scalability: Optimized for Zero Scale
Bolt.new scaffolds code designed to run in lightweight browser sandbox environments. Deploying that raw output to Netlify or Vercel without architectural refactoring frequently causes memory leaks, hydration mismatches, and sluggish Core Web Vitals.
TOOL PROFILE 4 • CLOUD DEV & HOSTING
Replit: Where It Fits and What Founders Miss
Replit occupies a different space. It provides a full cloud development environment with integrated hosting. Founders can build server-side applications with zero local setup and deploy with one click.
The Replit Blind Spot: Built-in hosting creates a false sense of production readiness. Just because your app is running on Replit does not mean it is hardened for real traffic. Replit imposes no security constraints on generated code; authentication, error handling, database indexing, and GTM telemetry remain 100% developer-dependent.
Launch Risk by Tool: The 5-Category Matrix
How Cursor, Lovable, Bolt.new, and Replit compare when audited across critical production dimensions:
| Risk Category | Cursor | Lovable | Bolt.new | Replit |
|---|
| Authentication Defaults | MEDIUM RISK Secure if prompted precisely; zero guardrails if prompts are vague. | LOW RISK Supabase Auth built-in; RLS active, but policy verification required. | HIGH RISK Auth varies widely per prompt; rarely hardened for multi-device sync. | MEDIUM RISK No defaults imposed; auth security depends 100% on developer code. |
| Data & Secret Handling | MEDIUM RISK No automated secret manager; requires strict developer hygiene. | MEDIUM RISK High abstraction makes inspecting client bundle boundaries harder. | HIGH RISK Highest likelihood of baking API keys directly into public browser bundles. | MEDIUM RISK Secrets handled in environment config; no linting for public leakage. |
| Error Management | MEDIUM RISK Graceful fallbacks require explicit prompts; absent by default. | MEDIUM RISK Functional error states, but often lacks sanitized API error responses. | HIGH RISK Minimal error handling; unhandled crashes expose internal stack traces. | MEDIUM RISK Developer-controlled; no automated error boundary generation. |
| Scalability & Load | LOW RISK Standard codebase architecture; zero platform lock-in. | MEDIUM RISK Supabase handles scale well, but requires connection pooling setup. | HIGH RISK Built for zero-scale browser demos; requires refactor for high traffic. | HIGH RISK Default shared hosting tiers throttle quickly under launch spikes. |
| GTM Readiness | MEDIUM RISK Zero automatic SEO or analytics; founder must explicitly prompt. | MEDIUM RISK Basic title tags generated; Open Graph and analytics require manual hookup. | HIGH RISK GTM infrastructure is completely absent from initial output. | HIGH RISK No default SEO optimization or event instrumentation. |
Which Tool You Choose Matters Less Than What You Review
Tool comparisons often miss the bigger picture: no AI builder—regardless of how sophisticated its prompts are—ships a production-ready application by default. Every single tool outputs a starting point.
Risk differences between tools are real, but the founder's responsibility stays identical: conduct a rigorous, structured pre-launch audit before real users connect their bank accounts or store sensitive data.
The 5-Point Pre-Launch Audit Verification Checklist:
- Test Auth as an Unaffiliated Stranger: Sign up in an incognito window with a fresh email. Verify password resets, OAuth redirects, and session expiry.
- Audit Client Bundle Boundaries: Inspect your compiled JavaScript in Chrome DevTools. Search for keywords like
sk_live_, service_role, and database connection strings. - Deliberately Trigger Error States: Submit malformed form inputs and invalid parameters. Confirm the user sees friendly feedback while raw stack traces stay suppressed.
- Verify Database Connection Limits: If using Supabase or serverless Postgres, confirm connection pooling is active before your announcement tweet goes live.
- Layer on GTM Infrastructure: Verify Open Graph preview images, canonical meta tags, and activation event tracking are configured before paying for traffic.
Built with Cursor, Lovable, or Bolt.new without a structured audit? Run Launchieve's free launch scan in under two minutes to catch critical blind spots before your users discover them.
Frequently Asked Questions
Is Lovable or Bolt.new safer for a production app?
Lovable carries lower launch risk than Bolt.new for most production use cases. Its native Supabase integration provides a real authentication and database layer that Bolt.new does not match by default. However, Lovable's abstraction layer still requires careful review of credential handling and RLS permissions. Bolt.new fits rapid zero-scale prototyping better than production deployment without extra security hardening.
What is the most secure AI builder for a real SaaS?
Cursor used by a developer with security awareness produces the most defensible output for a production SaaS, because a real codebase gives full visibility into authentication patterns, data handling, and error boundaries. For non-technical founders, Lovable paired with a focused pre-launch security review is typically a safer starting point than managing raw code.
Can Cursor build a production-ready app?
Yes. The operative word is “can.” Cursor is a code generation accelerator, not a production-readiness guarantee. Production readiness depends entirely on prompt quality, review discipline, and architectural knowledge. A skilled developer using Cursor with critical code review can produce enterprise-grade applications.
What AI builder is best for launching a startup in 2026?
There is no universal answer. Non-technical founders building a data-driven SaaS often find Lovable with Supabase offers the lowest floor risk. Technical founders seeking full architectural control prefer Cursor. Founders rapidly testing initial market interest can justify Bolt.new at the validation stage. Every path benefits from a structured pre-launch audit before shipping to real users.
Ship with Fewer Surprises
Speed matters only when week-one emergency patches are not part of your launch plan. Whether you built on Cursor, Lovable, or Bolt.new, verify your security boundaries and go-to-market layer before launching to paying customers.
L
Launchieve Technical Review Team
Technical Audit Engineers
We review AI-built codebases across security, infrastructure, APIs, and launch readiness. Our team has audited products built with Cursor, Lovable, Bolt.new, Replit, Supabase, Firebase, and mixed AI-assisted workflows. Every finding in this article comes from patterns observed in real technical reviews — not theoretical scenarios.